Third-Party Risk Management Software and Tools: How to Choose in 2026

Compare TPRM software by operating model, evidence quality, supplier participation, workflow fit, total cost and supply chain visibility.
Risk Ledger
|
Company
October 2, 2026
|
30
mins read
Third-Party Risk Management Software and Tools: How to Choose in 2026

Updated 1 October 2026: added evaluation scorecard, regulation and framework guidance, public sector coverage and methodology.

Quick answer

Third-party risk management (TPRM) software is a category of platform for assessing, monitoring and managing the security risk suppliers introduce, and the right third-party risk management tool is the one whose operating model fits your main constraint, not the one with the longest feature list.

  • Enterprise governance suites fit when supplier risk must sit inside wider GRC, procurement or audit, and one system of record matters most.
  • TPRM workflow platforms fit mature programmes that need detailed, configurable questionnaires, scoring and remediation.
  • Ratings and monitoring platforms fit broad outside-in visibility across large supplier populations, but don't evidence internal controls on their own.
  • Evidence and compliance platforms fit when faster due diligence and easier evidence sharing are the priority.
  • Network-led platforms fit when supplier chasing, repeated requests and visibility beyond direct suppliers are the hardest problems.

Then test every shortlisted vendor with one real supplier: evidence quality, supplier effort, what happens after a finding, and three-year cost.

Test every shortlisted vendor with one real supplier: evidence quality, supplier effort, what happens after a finding, and three-year cost.

Choosing TPRM software is not about finding the platform with the longest feature list. It's about finding an approach that fits how your team assesses suppliers, keeps evidence current and responds when risk changes.

Most platforms can organise assessments. The real test is what they change in practice: how much supplier chasing remains, how quickly you can establish exposure when an incident hits, and whether your team gets a clearer view of the suppliers and dependencies that matter most.

The point of risk management is to decide where limited time, attention and budget should go. TPRM software should make that prioritisation easier, not simply produce another score.

Jump to

  1. The five types of third-party risk management software
  2. Which type fits your programme?Tool
  3. Score your shortlistTool
  4. What "continuous" really means
  5. Self-assessment, ratings or verified evidence
  6. Regulation maps: financial services and public sector
  7. Questions to ask every vendor
  8. Which TPRM platformss fit which team
  9. How we approach TPRM at Risk Ledger
  10. FAQs
How we built this guide

We compare third-party risk management software by operating model rather than feature count. Each type of tool is assessed against the same criteria, using what security teams tell us they need, what platform users report in public reviews, and published product and regulatory information.

50+

conversations with security and risk teams evaluating third-party risk management software

17+

organisations, mostly in regulated sectors

40+

platforms mapped across G2, Gartner Peer Insights and Capterra

Read the full methodology

Scope

This guide covers security-led third-party risk management software. It does not evaluate the wider supplier risk market, where platforms also cover financial stability, ESG and geopolitical risk.

What we compared

Five types of third-party risk management tools, plus managed services and broader supplier intelligence as overlays, each assessed against the same criteria:

  • Supplier prioritisation and relationship context
  • Evidence quality, provenance and freshness
  • Supplier participation and effort
  • Findings, remediation and exceptions
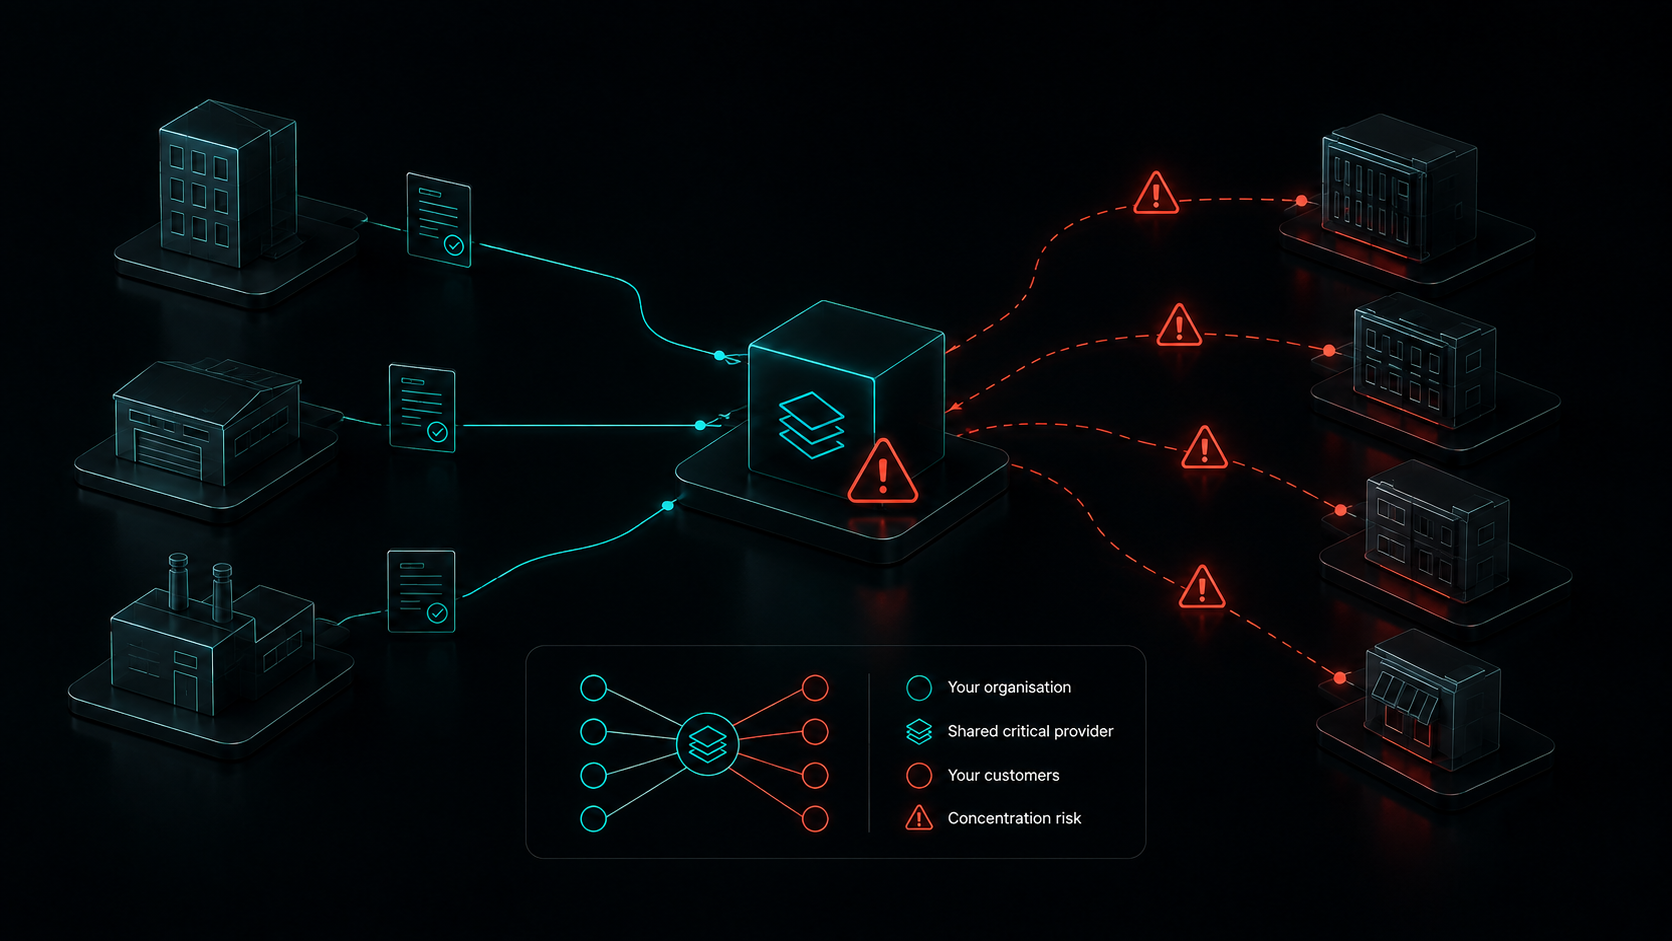
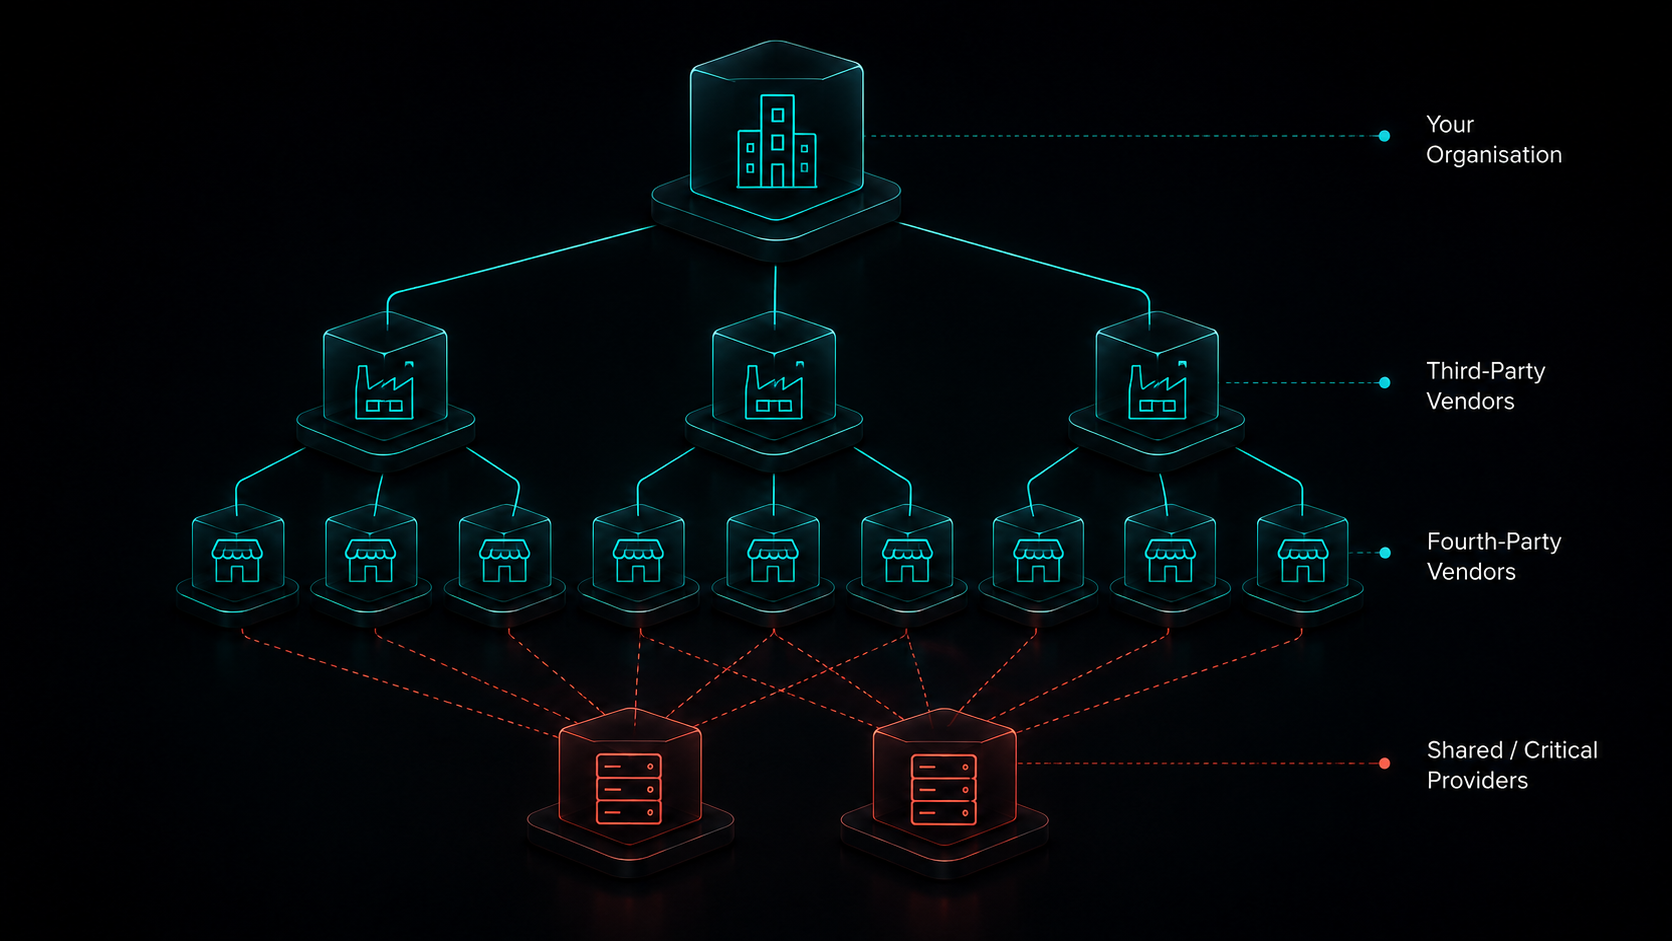
  • Visibility of nth-party dependencies and concentration risk
  • Workflow and integration fit
  • Implementation effort and total operating cost

Evidence, in order of weight

  • Official product documentation and published customer case studies
  • Regulatory and good-practice guidance, including NIST, the UK NCSC, DORA and the Cyber Assessment Framework
  • Recurring needs raised in our conversations with security and risk teams
  • Public platform reviews and category grids on G2, Gartner Peer Insights and Capterra, treated as a signal of user experience rather than proof of capability

How we kept it fair

Each type of tool is judged at its centre of gravity. A ratings platform isn't marked down for not being a governance suite, and a TPRM workflow platform isn't marked down for not owning procurement. Vendor information was checked in [month 2026] and is re-checked at each update.

Limitations

Our conversations lean towards UK financial services and other regulated sectors, so they show recurring patterns rather than a representative market survey. Capabilities, packaging and pricing change, so verify mandatory requirements through scripted demos, references and a proof of concept using your own supplier data.

Our point of view

We build a network-led TPRM platform, so we have a view on how supplier assurance should work. We've applied the same evidence standard to our own model as to every other, including where another approach may fit better.

‍

What is third-party risk management (TPRM) software?

Third-party risk management (TPRM) software is a category of platform that helps organisations identify, assess, monitor and manage the risk that suppliers and other third parties introduce. It centralises supplier inventories, security evidence, assessments, findings and monitoring, so security, procurement and risk teams can make consistent decisions across the whole supplier relationship.

TPRM software supports a set of recurring jobs across that relationship.

  • Before onboarding, it helps teams maintain a supplier inventory, classify suppliers by criticality and decide how much due diligence each one needs.
  • During due diligence, it collects security evidence such as questionnaire answers, certifications and policies, and records what the review found.
  • After approval, it monitors suppliers between reviews, flags expiring evidence, tracks remediation and triggers reassessment when something material changes. When an incident or new vulnerability emerges, it helps teams establish which suppliers and services are exposed.

Throughout, it produces the reporting that risk owners, auditors and regulators expect, and more advanced platforms also show the nth-party dependencies behind direct suppliers. A platform that only covers the first two stages digitises onboarding. The value of the category comes from carrying the same supplier context through the full lifecycle.
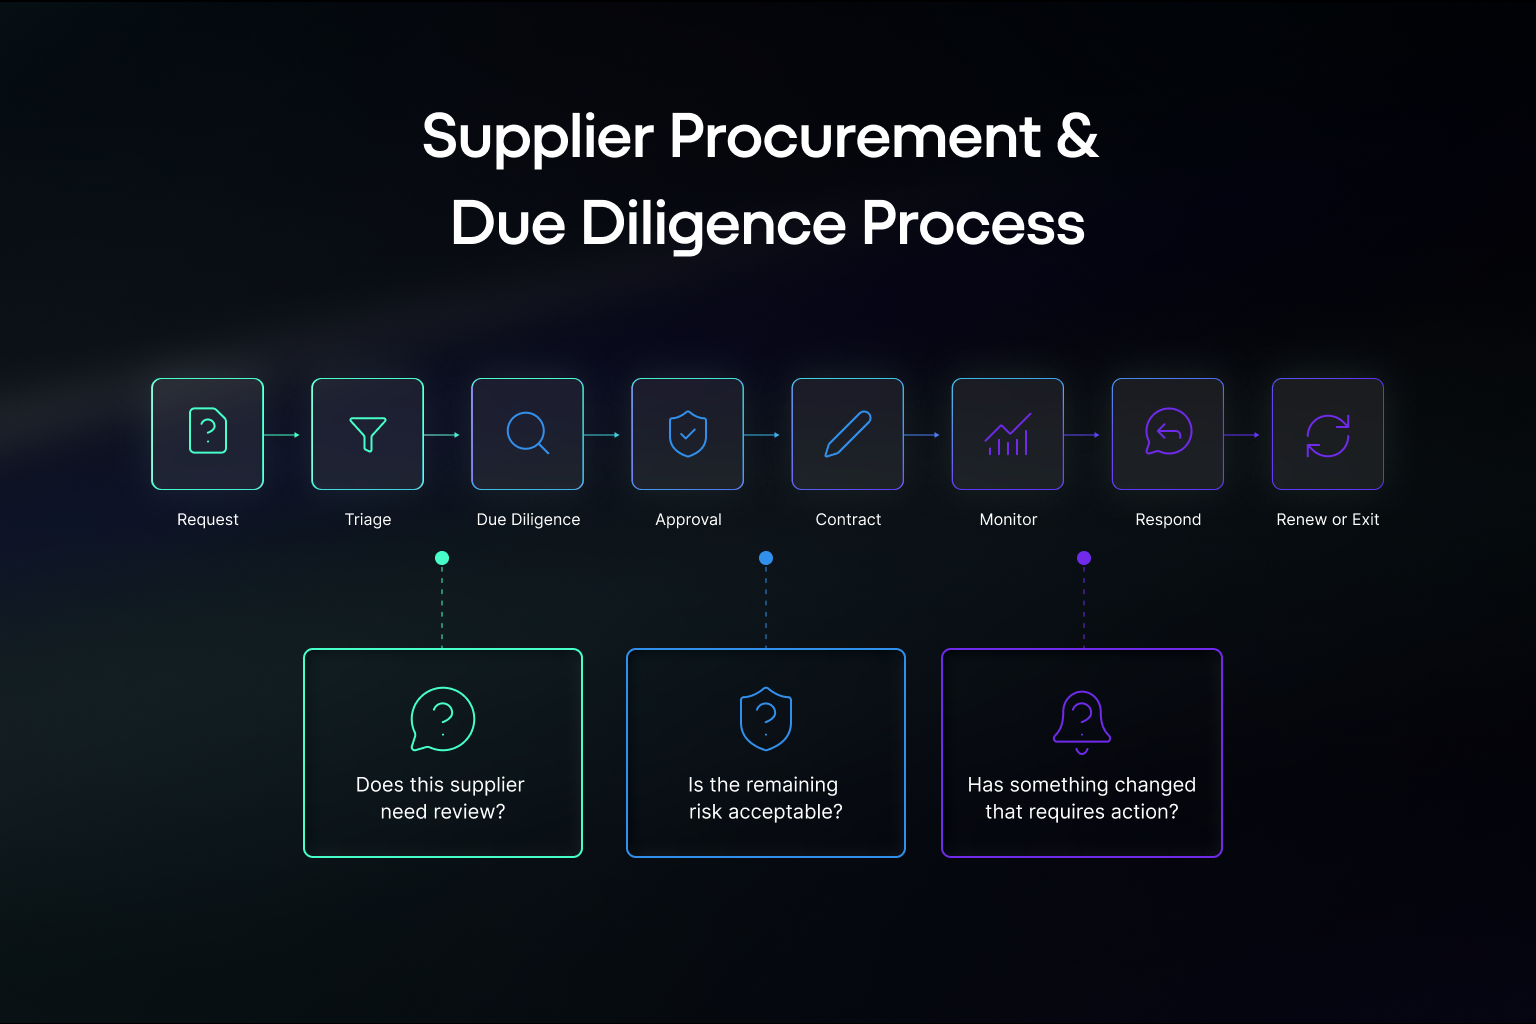
TPRM software lifecycle from supplier request and criticality assessment through due diligence, approval, monitoring, incident response and renewal

Security, third-party risk, procurement, GRC, compliance, privacy and internal audit teams all use TPRM software, often in the same organisation. The primary owner usually shapes the shortlist.

  • Procurement-led programmes tend to prioritise onboarding and contract workflow
  • GRC-led programmes prioritise controls and audit
  • Security-led programmes prioritise evidence quality, monitoring and incident response.

‍

TPRM software, TPRM tools and supplier risk management software: what's the difference?

TPRM software and TPRM tools usually mean the same thing: platforms for managing the security risk that suppliers and other third parties introduce.

Supplier risk management software is the broader category, covering financial, operational, ESG and geopolitical risk alongside cyber. Third-party risk assessment tools handle one stage of the job, and vendor risk management overlaps with TPRM almost entirely.

The terms matter because they put different products on the shortlist:

  • Platforms sold as supplier risk management software (such as Exiger, Interos and apexanalytix) are built around financial stability, sanctions, geopolitical exposure and physical supply chain disruption. They can be the right purchase for procurement and resilience teams, but cyber control assurance is rarely their deepest capability.
  • Platforms sold as TPRM software are built around security assessments, supplier evidence, findings and monitoring. Third-party risk assessment tools are narrower again. They handle questionnaires and evidence collection at due diligence, but not necessarily monitoring, remediation or reassessment after approval. If supplier security assurance is the main problem, compare TPRM platforms.

If your business needs financial, ESG and geopolitical risk in one system, evaluate broader supplier risk management platforms separately, and expect to pair them with a security-led process.

Vendor risk management (VRM) is largely a naming choice. Many platforms use VRM and TPRM for the same product, so treat the label as a search term rather than a difference in capability. Ownership is a better guide than terminology. When procurement leads the purchase, broader supplier risk platforms tend to appear on the shortlist. And when security leads, TPRM software usually does.

Terminology

TPRM terms at a glance

What each term usually covers, who tends to buy it and when it belongs on your shortlist.

Term
What it usually covers
Who typically buys
Compare it when
TermTPRM software and TPRM tools
What it usually coversSecurity assessments, supplier evidence, findings, remediation and monitoring across the supplier lifecycle.
Who typically buysSecurity, third-party risk and GRC teams.
Compare it whenSupplier security assurance is the main problem.
TermSupplier risk management software
What it usually coversFinancial stability, sanctions, ESG, geopolitical exposure and operational disruption, sometimes alongside cyber.
Who typically buysProcurement, supply chain resilience and enterprise risk teams.
Compare it whenYou need several types of supplier risk managed in one system.
TermVendor risk management (VRM) software
What it usually coversLargely the same scope as TPRM software. Many platforms use both terms for one product.
Who typically buysSecurity, procurement and compliance teams.
Compare it whenTreat it as TPRM software and judge the product, not the label.
TermThird-party risk assessment tools
What it usually coversQuestionnaires, evidence collection and scoring at due diligence.
Who typically buysSecurity teams formalising a first assessment process.
Compare it whenYou need a repeatable assessment now. Check what happens after approval.

Practical decision rule

Shortlist by the problem, not the label. If supplier security assurance is the job, compare TPRM software, whatever the vendor calls its product.

‍

What should TPRM software change?

TPRM software should remove repeated work, keep supplier evidence current and help the team act when risk changes. A platform that only digitises questionnaires and supplier registers makes the process tidier, but the decisions coming out of it are no better than before.

Most TPRM tools can send an assessment, store a document and produce a dashboard. That is the baseline, and it tells you little. The useful distinction is between platforms that improve how the existing process is administered and platforms that change the work the process depends on.

Admin gains are real: fewer spreadsheets, clearer ownership, an audit trail. But if suppliers still answer a fresh questionnaire for every customer, evidence still goes stale between annual reviews, and an incident still means emailing every supplier to ask whether they're affected, the team's workload has moved rather than shrunk.

Buyers tend to put this more plainly during evaluations. The questions that come up repeatedly are whether suppliers will actually fill it out, what still falls to the team after go-live, and whether the platform can show which suppliers are affected when something breaks. Those three questions are a better shortlisting test than any feature list.

TPRM evaluation

What a TPRM platform should change

Look beyond whether the platform can digitise the existing process. Test whether it removes repetitive work, improves the evidence available and helps the team act when risk changes.

Common TPRM process friction and the operational change a platform should create.

Current friction
What the platform should change
Current frictionThe same evidence is requested repeatedly
What the platform should changeSupplier information can be reused without removing your own review requirements.
Current frictionAssessments become stale
What the platform should changeEvidence has clear ownership, expiry dates and reassessment triggers.
Current frictionToo many suppliers appear equally important
What the platform should changeReview depth reflects supplier criticality, data access and operational dependency.
Current frictionMonitoring creates more noise
What the platform should changeAlerts lead to a clear decision, owner or remediation action.
Current frictionFindings sit in reports
What the platform should changeRisks, exceptions and remediation remain visible until they are resolved.
Current frictionAn incident creates a manual search
What the platform should changeSupplier exposure and affected services can be identified quickly.
Current frictionReporting measures completed activity
What the platform should changeReporting shows coverage, exposure, accepted risk and remediation progress.

Practical test

A stronger platform should improve the decisions coming out of the process, not simply provide a cleaner interface for administering it.

Questionnaires still have a role. They provide evidence about controls that can't be observed from outside, and both NIST and the NCSC  treat supplier questions as a legitimate assurance mechanism. The NCSC is also clear about the limits: answers represent a point in time, and the process is resource-intensive for suppliers and buyers alike. The problem is repeated one-to-one collection, inconsistent formats and answers treated as current long after the supplier's position may have changed.

Test the workflow, not the feature

Take one real supplier and ask each vendor to show:

  1. How the supplier is prioritised
  2. What evidence is already available, and what still needs requesting
  3. How uncertainty is recorded
  4. What happens when evidence expires
  5. How the team responds if that supplier is linked to an incident

Count the manual hand-offs and note who owns each step. If the demonstration ends at a score or dashboard, ask what happens next.

Software has limits here. If nobody owns supplier criticality or risk acceptance, a platform will make that missing ownership more visible but won't resolve it. And because headcount rarely grows as fast as the supplier population, the test of any platform is whether it creates time for analysis or just gives the same workload a new home.

‍

Where does third party risk management software fit in the supplier lifecycle?

TPRM software should sit wherever supplier-risk decisions are being made. That usually starts before onboarding, but it shouldn’t stop once the contract is signed. The same supplier context needs to carry through due diligence, approval, monitoring, incident response and renewal.

In reality, security is not always involved at the start.

Sometimes a supplier reaches the team before a commercial decision has been made. Sometimes the preferred option is already clear and the review is there to work out whether the risk is acceptable.

Both happen. The later the review starts, the less room there is to change direction if something material comes up.

A typical lifecycle looks like this:

  1. Supplier request or discovery
  2. Inherent-risk assessment and criticality
  3. Due diligence
  4. Risk approval and contract requirements
  5. Onboarding and remediation
  6. Monitoring and reassessment
  7. Incident response
  8. Renewal, replacement or exit

The value comes from joining those stages up.

A finding during due diligence may need to become a contract requirement. A change in evidence may need another review. An incident may require the team to work out which service depends on the supplier and who owns the relationship.

That doesn’t mean the TPRM platform needs to replace procurement, GRC, contract management or security operations. It means the hand-offs need to work.

What to test

Ask the vendor to take one supplier from initial request through approval, monitoring and incident response.

Pay attention to where information carries forward and where somebody still has to copy it into another system. Check what triggers reassessment, who owns each decision and whether the business context stays attached to the supplier.

The test is simple: does the platform help the organisation manage one connected supplier relationship, or several separate records that happen to use the same company name?

‍

What types of TPRM tools are available?

Most TPRM tools fall into five types: enterprise governance suites, TPRM workflow platforms, ratings and monitoring platforms, evidence and compliance platforms, and network-led TPRM platforms. They overlap at the edges, but each has a different centre of gravity. That shapes the evidence you get, the work suppliers do and how much administration stays with your team.

Products blur these lines. A workflow platform may ingest ratings, a ratings provider may add questionnaires, and a governance suite may offer managed assessments. The point is to identify where each product is strongest and test what it leaves behind, not to force it into one box.

TPRM platform landscape

The five types of third-party risk management software

Inclusion shows category placement only, not a recommendation.

  • 01

    Enterprise governance suites

    Manages governance and the system of record

    Strongest whenSupplier risk must sit inside wider GRC, procurement or audit

    Main trade-offHeavier implementation and lighter supplier-security depth

    OneTrustServiceNowArcherMetricStreamCoupaSAP Ariba
  • 02

    TPRM workflow platforms

    Manages assessments, findings and remediation

    Strongest whenMature programmes need configurable questionnaires and scoring

    Main trade-offCan preserve duplicated questionnaire work and add maintenance

    Mitratech PrevalentProcessUnityAravoVenminderCerta
  • 03

    Ratings and monitoring platforms

    Manages external cyber signals

    Strongest whenBroad, low-touch monitoring across large supplier portfolios

    Main trade-offLimited internal-control and relationship context

    SecurityScorecardBitsightUpGuardBlack KitePanorays
  • 04

    Evidence and compliance platforms

    Manages evidence reuse and sharing

    Strongest whenFaster due diligence and easier evidence sharing are the priority

    Main trade-offFreshness and customer-side workflow depth vary

    ProcessUnity Global Risk ExchangeWhisticVantaDrata
  • 05

    Network-led TPRM platforms

    Manages evidence, supplier participation and dependencies

    Strongest whenSupplier chasing, repeated requests and visibility beyond direct suppliers are the hardest problems

    Main trade-offNetwork coverage and standardisation must fit your programme

    Risk Ledger (our platform)

Practical decision rule

Do not compare every platform as though it solves the same problem. Start with its centre of gravity, then test the evidence it provides, the work it removes and the work it leaves behind.

Enterprise governance suites

Enterprise governance suites manage third-party risk as one module inside a wider GRC, IRM or procurement system. They're strongest when consolidation is the goal and one system of record across audit, privacy, procurement and enterprise risk matters most. The trade-off is depth and effort: implementation and administration can be heavy, and supplier-security assessment may be one module among many.

What to test: how much configuration the TPRM module needs, what suppliers see, and whether the evidence is richer than email would give you.

Our view

These platforms are strong at recording and governing supplier risk. Test whether they also generate current security evidence and get suppliers to participate, or whether they mainly hold the record of decisions made elsewhere.

TPRM workflow platforms

TPRM workflow platforms run the end-to-end assessment lifecycle as their core product, from intake and tiering through questionnaires, findings, remediation and renewal. They suit mature programmes with dedicated administrators and bespoke, weighted methodologies. The trade-off is that they can make the questionnaire model more efficient without changing it, and flexibility becomes maintenance.

What to test: time to useful supplier coverage, and who maintains questionnaires and scoring after launch.

Our view

Configurability is both the reason to buy one and the main thing to watch. Ask who will maintain the questionnaires, weights and mappings in year three, and whether suppliers experience each customer's assessment as a separate request.

Ratings and monitoring platforms

Ratings and monitoring platforms observe suppliers from outside, scoring internet-facing assets, vulnerabilities and configuration across large portfolios. They're strongest for rapid, low-effort coverage of thousands of suppliers and alerts when something observable changes. The trade-off is what the outside can't see: internal controls, and why a supplier matters to you.

What to test: how findings are attributed and disputed, and what happens between an alert and a decision.

Our view

Ratings are useful evidence, not complete assurance. They show what can be observed from outside, so plan for how findings will be combined with supplier evidence, validated and acted on.

Evidence and compliance platforms

Evidence and compliance platforms make existing security evidence easier to collect, reuse or share, through assessment exchanges or trust and compliance platforms. They're strongest when the same evidence is requested repeatedly and faster due diligence is the priority. The trade-off is freshness and depth: evidence reflects a point in time, and customer-side remediation workflows can be lighter.

What to test: how old the evidence is when you receive it, and what happens after you spot a gap.

Our view

Reuse is a real improvement over repeated questionnaires. The next question is whether you're receiving a report that starts ageing on the day it's issued, or a relationship where evidence, findings and remediation keep moving.

Network-led TPRM platforms

Network-led TPRM platforms connect customers and suppliers on a shared platform. Suppliers maintain one reusable security profile, each customer applies its own policies, and the connections show dependencies beyond direct suppliers. They're strongest when supplier chasing, duplicated assessments and concentration risk are the main problems. The trade-off is coverage and standardisation.

What to test: network coverage of your actual supplier list, and the onboarding route for suppliers not yet represented.

Our view

This is the model we build, so weigh this note accordingly. Its value rises with network coverage, which makes the honest first test simple: check how many of your suppliers are already represented, and what happens for the ones that aren't.

Managed services and broader supplier intelligence

Two things often appear on TPRM shortlists without being types of TPRM tool.

Managed services are a delivery model. Providers run assessments, review evidence and chase suppliers on your behalf, and any of the five types can come with one. If the real constraint is people rather than process, a managed service can be better advice than new software. Ask whether you're buying software, people or both, and who holds the programme's knowledge if the service changes.

Broader supplier intelligence platforms cover financial, ESG, geopolitical and physical supply chain risk. They solve a wider problem than security-led TPRM and are worth evaluating separately if that wider problem is yours.

Comparing specific vendors?

Our guide to the best third-party risk management software compares individual platforms, their operating models and the use cases each fits best.

Compare TPRM vendors

‍

How to choose the right TPRM operating model

Choosing a TPRM operating model means matching the type of tool to the constraint that's actually limiting your programme. That constraint might be supplier chasing, stale evidence, governance, external visibility or internal capacity. Start with the hardest recurring job your team has to do, then check that the rest of the supplier lifecycle still works.

"We need better TPRM" is too broad to shortlist against, so be specific about where the process breaks. For some teams it's collecting evidence: the same questions sent to the same suppliers, answered slowly or not at all. For others it's deciding which suppliers matter, keeping assessments current, managing remediation, or working out which suppliers are exposed when a vulnerability or outage hits.

Each of these points to a different type of tool. A team buried in governance and audit requests needs something different from a team that can't get suppliers to respond. Then ask who will run the platform day to day. Someone has to onboard suppliers, review evidence, investigate alerts, manage remediation and maintain integrations. A capable platform is the wrong choice if it assumes time or specialist ownership your team doesn't have, so assess the ongoing operating load, not just the implementation project.

What usually triggers the decision

Across the conversations behind this guide, four triggers come up repeatedly:

  • A regulation makes the status quo untenable. DORA is the one cited most often in financial services.
  • An incumbent tool is discontinued or reaches renewal.
  • A new CISO or security lead arrives with a mandate and budget.
  • Underneath all three, most commonly, a team of one or two people can no longer run questionnaires by hand in Word and Excel.

The trigger shapes the shortlist more than buyers expect. A regulatory deadline favours tools that produce audit-ready evidence quickly, and a tool replacement favours low migration risk. A new mandate often brings ambition beyond what the team can yet operate, which is worth naming before the first demo.

Match the model to programme maturity

Spreadsheet-led programmes. Spreadsheets aren't automatically wrong. For a small supplier population with a clear owner, a well-kept spreadsheet can be the right starting point. Buying a platform before you have a supplier inventory and agreed tiering often stalls. Spreadsheets become the wrong model when supplier volume, evidence freshness, regulatory expectations or incident response outgrow what the team can maintain by hand.

Growing security-led programmes. These teams are past the basics but still fighting supplier chasing, inconsistent evidence and low engagement. The priority is evidence collection, supplier experience and getting reassessment to happen on schedule, rather than adding governance to a process that isn't yet running smoothly.

Mature enterprise programmes. These need governance across business units, audit trails, configurable approval routes and integration with GRC, procurement or ticketing systems. Dependency mapping and concentration-risk analysis become genuinely useful at this stage, once the supplier inventory is reliable enough to trust the output.

Advanced programmes. These are pushing beyond point-in-time assessment towards continuous assurance, with nth-party visibility, concentration risk and emerging-threat response as the priorities.

A platform built for one stage isn't wrong for another, but the mismatch shows. A highly configurable enterprise platform can slow a small team down before it delivers value, and a lightweight tool can run out of road once audit requirements grow. Buy for where the programme is now, not where you expect it to be in two years.

Interactive tool

Which type of TPRM platform fits your programme?

Answer five questions. The tool scores each type of software against your answers and shows how it reached the result.

1What's the biggest problem in your current process?
2Who leads the purchase?
3How much capacity does your team have?
4How many suppliers are in scope?
5How important is visibility beyond your direct suppliers?

‍

How to evaluate TPRM software: a weighted scorecard

A TPRM scorecard weights the criteria that matter most to your programme and scores each vendor against them, with mandatory requirements treated as pass or fail.

Weighting stops every stakeholder's wish list from counting equally, and it makes the final decision easier to defend to procurement, audit and the board. Unweighted requirement lists favour the broadest platform, because every extra feature earns a tick whether or not it touches your actual problem.

Start from the bottleneck you identified when choosing an operating model and weight those criteria most heavily. If supplier chasing is the main burden, participation should count for more than reporting. If governance across business units is the issue, the reverse applies. Separate mandatory requirements first.

A vendor that fails one is out, however well it scores elsewhere, because strength in one area can't make up for a requirement you can't operate without. Then score from evidence rather than presentations: a demo using your own suppliers, a reference call with a team of similar size, or a proof of concept. Include the people who will run the process day to day, not just the buying team. Analysts and likely administrators often spot practical problems a standard demo hides.

Evaluation framework

Ten criteria for scoring third-party risk management software

Starting weights out of 100. They're a neutral default, so re-weight them around your own bottleneck.

  1. 15weight

    Evidence quality and provenance

    What to prove: where each piece of evidence comes from, how it's validated, what it covers and how disputes are handled.

  2. 15weight

    Findings, remediation and exceptions

    What to prove: every finding has an owner, deadline and escalation route, and every exception has a rationale and an expiry date.

  3. 10weight

    Supplier prioritisation

    What to prove: different review paths for critical and low-risk suppliers, and assessment at product or service level rather than company level only.

  4. 10weight

    Supplier participation and effort

    What to prove: how much each supplier must do, whether evidence can be reused, and what happens when a supplier isn't on the platform or won't respond.

  5. 10weight

    Evidence freshness and continuous assurance

    What to prove: expiry dates, material-change triggers and reassessment, not just the volume of alerts.

  6. 10weight

    Workflow and integrations

    What to prove: the path from procurement request to assessment, finding and GRC or ticketing record, and what stays manual.

  7. 10weight

    Implementation and adoption

    What to prove: a week-by-week plan and the date priority suppliers will actually be covered, not just configured.

  8. 10weight

    Total operating cost

    What to prove: three-year cost including services, data feeds, supplier chasing, analyst time and exit.

  9. 5weight

    Dependency and concentration visibility

    What to prove: which nth-party relationships are visible, how they were established and how they're used during an incident.

  10. 5weight

    Reporting and governance

    What to prove: views for analysts, risk owners, auditors and boards that trace back to the evidence behind each figure.

‍

Continuous assurance vs point-in-time assessment: what "continuous" really means

Point-in-time assessment checks a supplier at onboarding and at scheduled intervals. Continuous assurance keeps the evidence behind that decision current between reviews, and triggers action when something material changes. Most TPRM software now claims the second, so the more useful question to ask is which kind of "continuous" a vendor actually means.

A questionnaire answered in March describes the supplier in March. Between reviews, a supplier can change hosting provider, add a subprocessor, let a certification lapse, lose the person who owned security or sit on an unpatched vulnerability, and none of it appears until the next cycle.

That's why regulators and buyers are pushing from annual questionnaires towards ongoing assurance. It's also why the term needs pinning down, because vendors use it for very different things. For some it means daily external scans. For others it means a reminder when a document expires, or a reassessment every six months.

Each is useful, but they answer different questions, and none of them alone tells you whether a supplier's internal controls still hold today. It's a fair challenge to raise in an evaluation. In one financial services evaluation we've seen directly, the buyer's own security team questioned whether a six-monthly reattestation counted as continuous at all.

Continuous monitoring

Seven things vendors mean by "continuous"

Each is useful. None is complete on its own.

  1. Continuous external scanning

    Tells youObservable technical changes on a supplier's internet-facing assets.

    MissesInternal controls, and why the supplier matters to you.

  2. Document expiry alerts

    Tells youWhen a certification, policy or report has lapsed.

    MissesAnything that changed before the document expired.

  3. Supplier-reported control changes

    Tells youChanges the supplier updates between reviews.

    MissesChanges the supplier doesn't report, so ask what prompts an update.

  4. Scheduled reassessment

    Tells youA full refresh of the supplier's position on a fixed cycle.

    MissesEverything that happens between cycles.

  5. Triggered reassessment

    Tells youA fresh review when an incident, acquisition or new service changes the risk.

    MissesAny change nobody defined as a trigger in advance.

  6. Threat intelligence matched to suppliers

    Tells youWhich suppliers may be affected by a newly disclosed vulnerability or campaign.

    MissesConfirmation, which still has to come from the supplier.

  7. Dependency-aware exposure analysis

    Tells youWhere one issue reaches several services through shared providers.

    MissesAnything outside the relationship data, which must itself stay current.

Practical test

Ask each vendor which of these they mean. Then ask which evidence updates without anyone acting, which needs the supplier to do something, and which waits for the next review.

Assuring existing suppliers, not just new ones

Most TPRM programmes are strongest at onboarding. The harder half is the supplier approved years ago under an older process, still delivering a critical service, whose evidence nobody has looked at since.

Guidance treats this as a distinct job. The NCSC's guidance on assessing supply chain cyber security has a separate stage for bringing existing suppliers into the approach. It recommends reviewing existing contracts at renewal, or sooner for critical suppliers.

For public bodies working to the Cyber Assessment Framework, Principle A4 asks organisations to know the extent of their supply chain, including subcontractors, and to account for supply chain incidents in their incident management. Onboarding checks alone can't demonstrate either.

Financial services faces the same expectation: DORA's Article 28 frames ICT third-party risk as something managed across the whole contractual lifecycle, from pre-contract due diligence through ongoing monitoring to exit.

Continuous doesn't mean constant. Re-reviewing every supplier every month would bury the team and the suppliers. Proportionate assurance keeps low-risk suppliers on a lighter cycle, watches critical suppliers more closely, and sets clear triggers that pull any supplier forward when something changes.

What to test

  • Which evidence updates on its own, which needs the supplier to act, and which waits for the next review
  • What triggers a reassessment, and who defines those triggers
  • How existing suppliers are brought into the process, not just new ones
  • What happens to an alert: who owns it, what decision is recorded, and where

‍

Will suppliers participate, and how much work will they do?

Supplier participation is part of a TPRM platform's performance, not an implementation detail. A platform with strong customer workflows still fails if suppliers struggle to join, repeat work they've already done for other customers, or have little reason to keep their information current.

"Will our suppliers actually fill this out?" is one of the first questions buyers ask, and it's the right one. Non-engagement comes up in almost every evaluation we see. It takes the form of suppliers that don't respond, vendors reachable only through a managed service provider, and large providers that decline customer-specific questionnaires outright.

The cost lands on both sides. Your team spends time chasing, while suppliers deprioritise requests, rush answers or send whatever evidence is easiest to find. The result may be a completed assessment, but not better assurance. Evidence reuse reduces that friction, provided you can still apply your own policies, criticality and review requirements.

A supplier shouldn't have to rebuild the same security profile for every customer, but you still decide whether the evidence is enough for your relationship. Commercial terms matter too. In one evaluation we've seen directly, the buyer ruled out a platform that charged suppliers to join - their reasoning was that suppliers who weren't responding for free wouldn't start once they had to pay.
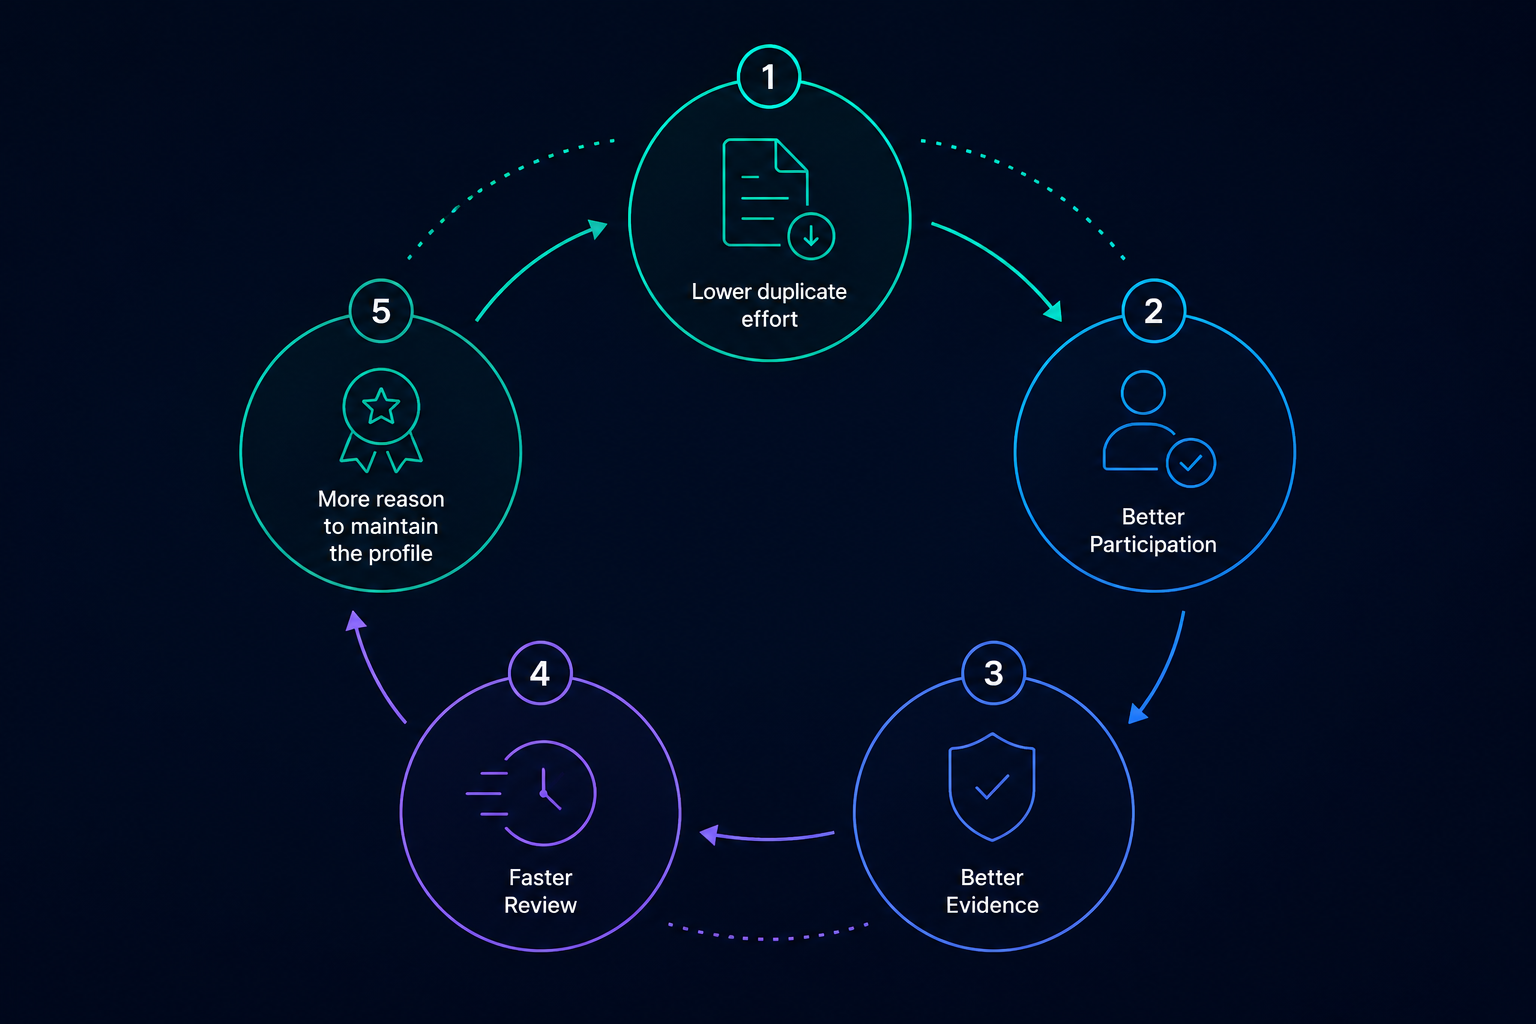
Supplier Cycle

Test four supplier scenarios

Ask each vendor to demonstrate:

  1. A supplier already represented on the platform
  2. A new enterprise supplier
  3. A small supplier without a dedicated security team
  4. A supplier that refuses to participate

For each one, look at the onboarding effort, the support available, the reminder process, whether evidence can be reused and what the fallback is. Then ask for adoption measures from customers like you: invitation acceptance, response time, profile completion, evidence freshness and reassessment completion. Supplier adoption should be measured, not assumed.

Proportionate assurance for small and non-IT suppliers

A local contractor or specialist service provider may have no security team, no certifications and nobody equipped to answer a long technical assessment, yet still hold sensitive data or access to a system you rely on. Sending them the same questionnaire as a cloud provider produces either silence or answers nobody can rely on.

Proportionate assurance tiers suppliers by potential harm, access and dependency rather than contract value, then sets a lighter route for the lowest tier. Cyber Essentials is a useful baseline here, because it gives you evidence that fundamental technical controls are in place against common, untargeted attacks. It's a floor, not a ceiling. A supplier with privileged access needs more.

Councils and government departments feel this most sharply. They combine a long tail of small local suppliers with a handful of critical technology providers, and the same supplier often receives near-identical questionnaires from several public bodies. Reusing evidence reduces that duplication, while accountability for each risk decision stays with the organisation making it. Every route also needs a fallback for suppliers that genuinely can't use the standard process, such as a short form, a call or a certification check.

Proportionate assurance

Three tiers of supplier assurance

Assurance depth rises with potential harm, access and dependency.

  • Tier 1

    Light touch

    Use when

    The supplier has no access to your systems or sensitive data and is easy to replace.

    Ask for

    A short declaration, named security contact and ownership details, plus Cyber Essentials if they hold it.

  • Tier 2

    Standard

    Use when

    The supplier handles limited data or provides a service that matters but has alternatives.

    Ask for

    A proportionate questionnaire, Cyber Essentials or equivalent, and commitments on incident notification.

  • Tier 3

    Enhanced

    Use when

    The supplier has access to systems or sensitive data, or is a critical dependency that's hard to replace.

    Ask for

    A full assessment with supporting evidence, independent certification, visibility of key subcontractors and ongoing monitoring.

Practical decision rule

Tier by potential harm, access and dependency, not contract value. A low-value supplier with administrative access to your network belongs in the top tier.

‍

Can TPRM software show risk beyond your direct suppliers?

Some TPRM software can show nth-party relationships, meaning your suppliers' suppliers and beyond, and the shared providers that create concentration risk across several direct suppliers. Platforms differ in where that relationship data comes from, how current it is, and whether you can use it during an incident.

Two definitions first:

  • Nth-party risk is risk that reaches you through your suppliers' own suppliers.
  • Concentration risk is what happens when several of your suppliers, or several of your important services, depend on the same provider.

A supplier register tells you who you contract with. It doesn't tell you who those suppliers depend on. The MOVEit breach in 2023 showed the difference. Many UK organisations found their staff data had been taken not because they used MOVEit themselves, but because their payroll provider did. When a shared provider fails, the useful question isn't whether a supplier is on your register. It's where your exposure sits, through whom, and which services need attention first. Answering that from a register means emailing every supplier and waiting for replies. Answering it from relationship data means filtering a list you already hold, provided that data is current. The difference is measured in days during an incident, and in credibility when the board or a regulator asks how quickly you knew.

Financial services feels this first because regulators ask for it directly. DORA requires financial entities to assess ICT concentration risk, and UK firms work under the FCA and PRA operational resilience rules, which expect them to map the third parties behind their important business services. Concentration risk is one of the reasons buyers we speak to give for moving visibility beyond direct suppliers up their list.

The public sector has its own version. In June 2024, a ransomware attack on Synnovis, a pathology provider serving several south-east London NHS trusts and GP services, disrupted blood testing and forced thousands of appointments and procedures to be postponed. One supplier, many public bodies. The same pattern applies to a department and its arm's-length bodies, or to councils in a region sharing an IT or payroll provider. Each relationship can look acceptable on its own, while the shared dependency concentrates risk across all of them.

Every supply chain map is only as complete as the relationships behind it. Visibility beyond the first tier depends on suppliers declaring who they rely on, or on external data that can be wrong or out of date, and most programmes only need it for the critical part of the supply chain. Build it once your supplier inventory and tiering are reliable, not before.

Nth-party visibility

Four sources of supplier relationship data

Ask which source sits behind every relationship a platform shows you.

  • Confirmed by both parties

    Highest confidence

    Both sides of the relationship confirm it exists.

    Shows you: dependencies you can act on with confidence.

    Watch for: coverage limited to organisations that participate.

  • Declared by suppliers

    Good confidence

    The supplier states which providers it relies on.

    Shows you: real business relationships, including ones invisible from outside.

    Watch for: depends on participation, so ask how often declarations are refreshed.

  • Inferred from external data

    Lead to confirm

    Technology fingerprinting, DNS, hosting and similar public signals.

    Shows you: broad coverage with no supplier effort.

    Watch for: shows technologies in use, not necessarily business relationships, and can be wrong.

  • Purchased intelligence

    Check the method

    Third-party databases of corporate and supply relationships.

    Shows you: coverage at scale across many organisations.

    Watch for: freshness and collection methods are often opaque.

Practical decision rule: treat an inferred relationship as a lead to confirm, not a fact. Use confirmed and declared relationships for decisions you may need to defend.

What to test

  • Show a real concentration finding, with several of your suppliers relying on one provider.
  • During a live incident, show how the team moves from an alert to a confirmed list of affected suppliers and services.
  • Show how each relationship is established and how often it's refreshed.
  • Show whether relationships link to your business services, not just to supplier names.

‍

Self-assessment, security ratings or verified evidence?

Self-assessment, security ratings and independent certification each answer a different question about a supplier, and none answers all of them. Verified evidence connects supplier-provided answers, supporting documents, external findings and the context of your relationship, so a TPRM decision rests on more than one source.

A security rating is an outside-in score of a supplier's observable cyber posture. TPRM is the wider process of assessing, deciding on and managing supplier risk, and a rating can be one input to it. Ratings are genuinely useful. They cover thousands of suppliers with no supplier effort, spot observable changes quickly and give a consistent benchmark. What they can't see is inside the organisation: whether access is reviewed, backups are tested or incident response has been rehearsed. They also can't tell that one supplier holds your customer data while another delivers stationery.

Questionnaires have the opposite strengths. They reach internal controls a scanner can't, but they rely on the supplier's word and start ageing the day they're answered. Treating either as complete assurance is the mistake. The stronger model uses each where it's strongest and checks them against each other.

Evidence sources

What each evidence source can answer

No single source answers every question a supplier decision depends on.

Question Questionnaire Documents and certification External rating Relationship context

Are the right internal controls in place?

Questionnaire: As claimed (answers it) Documents: Within audit scope (partly) Rating: Not visible (can't answer it) Context: Not its job (can't answer it)

Are those controls still working today?

Questionnaire: Point in time (can't answer it) Documents: Until expiry (partly) Rating: Observable controls only (partly) Context: Not its job (can't answer it)

Is anything exposed on the internet?

Questionnaire: Only if disclosed (can't answer it) Documents: Rarely covered (can't answer it) Rating: Core strength (answers it) Context: Not its job (can't answer it)

Has anyone independent checked?

Questionnaire: Self-declared (can't answer it) Documents: Auditor or certifier (answers it) Rating: Independent, outside-in (partly) Context: Not its job (can't answer it)

Does it matter for our relationship?

Questionnaire: If service-specific (partly) Documents: Generic scope (can't answer it) Rating: Same score for every customer (can't answer it) Context: Data, access, criticality (answers it)

Practical decision rule: no single column fills every row. Verified evidence comes from combining sources and recording where they disagree.

What verified evidence looks like in practice

When an external scan flags an exposed service, the useful next step is to link it to the supplier's answer on patching or asset management. Then ask the supplier to confirm, fix or explain it, and record the outcome. A finding that contradicts a self-assessment answer is often the most valuable signal in the whole process, because it shows where the supplier's view of itself and the observable reality differ.

Platforms vary widely here. Some place questionnaire results and ratings side by side. Fewer connect the two, let the supplier dispute a finding with evidence, and keep a record of who reviewed it and what was decided. That record matters most when you need to show an auditor or reviewer that controls were checked rather than simply declared, which public bodies working to the CAF and regulated firms both face.

Combining sources creates its own work. Someone has to review the disagreements, and a blended score can hide uncertainty rather than resolve it. If a platform offers a combined score, ask to see the inputs behind it.

What to test

  • Show how an external finding links to the relevant assessment answer.
  • Show how a supplier disputes or explains a finding, with evidence.
  • Show where disagreement between sources is recorded.
  • Show who reviews the evidence, who makes the decision, and the audit trail behind both.
  • Show the inputs behind any combined score.

‍

How TPRM software supports regulation and frameworks

TPRM software doesn't make an organisation compliant. What it can do is help you produce, maintain and retrieve the evidence your obligations require, and make the decisions behind that evidence traceable. The compliance judgement stays with your team, your regulator and your auditor.

Vendors often blur three different things:

  • Framework mapping links assessment questions to obligations such as DORA or the Cyber Assessment Framework
  • Evidence management keeps the evidence behind those answers current, owned and retrievable
  • Compliance judgement decides whether the result meets the obligation. Most platforms offer the first, the strongest help with the second, and none can do the third for you.

Evidence management keeps the evidence behind those answers current, owned and retrievable. Compliance judgement decides whether the result meets the obligation. Most platforms offer the first, the strongest help with the second, and none can do the third for you. A platform that maps every question to every framework still leaves you exposed if the evidence behind the answers is two years old and nobody can say who accepted the risk.

Ask the vendor to produce, during the demo, the evidence pack for one critical supplier exactly as a regulator or reviewer would request it. That means the current assessment, its sources, open findings, accepted risks with their owners, and the history of each decision.

Framework mapping links assessment questions to obligations such as DORA or the Cyber Assessment Framework. Evidence management keeps the evidence behind those answers current, owned and retrievable. Compliance judgement decides whether the result meets the obligation. Most platforms offer the first, the strongest help with the second, and none can do the third for you. A platform that maps every question to every framework still leaves you exposed if the evidence behind the answers is two years old and nobody can say who accepted the risk. The useful test is practical. Ask the vendor to produce, during the demo, the evidence pack for one critical supplier exactly as a regulator or reviewer would request it. That means the current assessment, its sources, open findings, accepted risks with their owners, and the history of each decision.

Financial services: Financial services: DORA and FCA and PRA operational resilience

DORA applies to EU financial entities, including the EU operations of UK groups. Article 28 treats ICT third-party risk as something managed across the whole relationship, from pre-contract due diligence through monitoring to exit, backed by a register of all ICT contractual arrangements. Article 29 adds an assessment of ICT concentration risk.

FCA and PRA operational resilience rules (PS21/3) have been fully in force since the transition period ended on 31 March 2025. Firms must map the people, processes, technology, facilities and information behind each important business service, including third parties. The FCA is explicit that if a third party causes a firm to breach an impact tolerance, the breach is the firm's responsibility.

Material third-party reporting comes next. The FCA's PS26/2 and the PRA's PS7/26 come into force on 18 March 2027. Firms will have to notify the regulators when they enter into or significantly change a material third-party arrangement, and maintain and annually submit registers of those arrangements. The FCA has said this register data will also help regulators identify future critical third parties, the large providers overseen directly under a separate regime.

Regulation map: financial services

What third-party risk management software should help you evidence

ObligationEvidence the software should help produceStays your judgement

DORA Article 28ICT third-party lifecycle and register

Software should help produceRegister of ICT arrangements, due diligence records, monitoring history and exit plans for each provider.

Stays your judgementWhich functions are critical or important, and whether residual risk is acceptable.

DORA Article 29ICT concentration risk

Software should help produceAnalysis of shared ICT providers across your suppliers and the services that depend on them.

Stays your judgementWhether a concentration is acceptable, and what you do about it.

FCA and PRA operational resiliencePS21/3 mapping of important business services

Software should help produceThe third parties behind each important business service, with current evidence and remediation status.

Stays your judgementImpact tolerances, and whether you can stay within them.

FCA PS26/2 and PRA PS7/26Material third-party reporting from 18 March 2027

Software should help produceA maintained register of material arrangements and a record of significant changes, ready to notify and submit. Regulators will also use this data to identify future critical third parties.

Stays your judgementWhich arrangements count as material.

Summary for evaluation purposes, not legal advice. Check obligations against the current regulatory text for your firm.

Public sector: CAF, GovAssure and audit evidence

The Cyber Assessment Framework (CAF) reached version 4.0 in August 2025. Principle A4 covers supply chain. Its good-practice indicators include knowing the extent of the supply chain behind your essential functions, including subcontractors, and making sure your incident management accounts for incidents that start in the supply chain.

GovAssure is the government's scheme for assessing critical systems against the CAF. Government organisations must use it for OFFICIAL systems considered government-sector critical national infrastructure, and lead departments support their arm's-length bodies through the process. Most organisations also undergo an independent assurance review, which assesses supply chain outcomes alongside the rest of the CAF.

Supply chain scrutiny is increasing. The government's digital roadmap sets December 2026 as the point when foundations to strengthen supply chain security should be in place. It describes clearer mapping of government supply chains and enforced baseline security standards. For public bodies, the practical requirement is audit-ready evidence that supplier controls were checked, not just declared. That means named owners, remediation history and decisions that can be retrieved when a reviewer asks.

Regulation map: public sector

What TPRM software should help you evidence

ObligationEvidence the software should help produceStays your judgement

CAF A4.aUnderstanding your supply chain

Software should help produceAn inventory of suppliers behind each essential function, including known subcontractors.

Stays your judgementWhether your understanding meets the target CAF profile.

CAF A4.aSupply chain incidents

Software should help produceSupplier incident contacts, notification commitments and fast exposure analysis when an incident starts.

Stays your judgementHow you respond, and who you inform.

GovAssureIndependent assurance review

Software should help produceAn evidence pack showing supplier controls were checked, with sources, findings and remediation.

Stays your judgementYour CAF profile and self-assessment.

Existing suppliersNCSC supply chain guidance

Software should help produceReassessment records for existing contracts, starting with critical suppliers.

Stays your judgementWhich contracts to revisit first, and when.

Internal and external auditDecision traceability

Software should help produceNamed owners, remediation history and accepted risks with expiry dates.

Stays your judgementRisk appetite and acceptance decisions.

Summary for evaluation purposes, not formal guidance. Check against current NCSC and Government Security Group material for your organisation.

‍

What happens after a finding? Workflow, governance and reporting

A finding is where TPRM software either earns its keep or becomes a reporting tool. The platform should give every finding an owner, a deadline and a route to remediation or documented risk acceptance. It should then pass the outcome into procurement, GRC and ticketing systems without anyone re-keying it.

Supplier risk runs across teams that rarely share a system. Procurement may sign a supplier before security is involved, and a late review leaves less room to change course. And a finding at due diligence may need to become a contract clause, an exception may need GRC approval, and an incident may require working out which service depends on the supplier, something nobody recorded at onboarding.

Each hand-off is a chance to lose context. A finding emailed to procurement arrives without its evidence, and a risk accepted in one system expires unnoticed in another.

TPRM software doesn't need to replace your procurement or GRC platform to fix this. It needs to make the hand-offs reliable, so the same supplier context travels with each decision. The test is simple - follow one supplier from request to renewal and ask whether you're looking at one connected relationship, or several separate records that happen to share a company name.

Findings and remediation

The life of a finding

What good looks like at each step, from detection to the record an auditor can follow.

  1. Detected

    Raised from an assessment, document review, external scan or threat alert, and linked to its evidence.

  2. Assigned

    A named internal owner and a supplier contact, with a deadline set by severity.

  3. Supplier responds

    The supplier fixes it, disputes it with evidence or proposes a compensating control.

  4. Resolved or accepted

    Closed with evidence, or accepted by a named risk owner with an expiry date.

  5. Recorded and reported

    Decision history kept, outcome passed to GRC or ticketing, and exposure reporting updated.

Practical decision rule: if any step happens outside the platform, check how the outcome gets back in. That return trip is where most findings quietly go missing.

The integrations that matter

Integration lists are long and mostly beside the point. The integrations that matter connect the start of a supplier relationship to the decisions made about it:

  • Procurement or contract intake, so new suppliers enter the process before signature
  • The GRC risk register, so accepted supplier risks sit alongside other enterprise risks
  • Ticketing, so remediation and internal actions are tracked where teams already work

Asset and identity inventories help link suppliers to the systems and data they touch. Ask to see each integration working end to end in the demo, using your own field names, rather than as a logo on a slide. An API means an integration project is possible. It doesn't mean the integration already exists.

Reporting that shows control, not activity

Completed assessments measure effort. Boards and regulators ask a different question: which critical suppliers are covered, where material exposure sits, and which risks have been accepted, by whom and until when.

Different audiences need different views of the same evidence:

  • Analysts need overdue evidence, open findings and supplier responses.
  • Risk owners need exposure by business service and the risks they've accepted.
  • Executives need coverage of critical suppliers, material exposure and how both are trending.

Every figure should trace back to the evidence behind it. Buyers often need this reporting to build the internal business case in the first place, so test it early, not after go-live.

Group and federated structures

Groups add a governance layer. A government department and its arm's-length bodies often share suppliers while each organisation stays accountable for its own risk decisions, and the same is true of a regional group of councils. GovAssure reflects this structure, with lead departments supporting their arm's-length bodies through the process.

The platform question is whether a central team can set policy and see concentration across the group while each entity keeps its own assessments, risk appetite and decisions. Test permissions, escalation routes and group-level reporting. Check that reusing one entity's assurance doesn't quietly transfer accountability to it. The same model may suit financial services groups with several regulated subsidiaries, though it's a less established pattern there than in central government.

What to test

  • Who owns the finding, and can the supplier respond with evidence?
  • Is there a deadline, an escalation route and a record of compensating controls?
  • Can a risk be accepted with a named owner and an expiry date?
  • Does the outcome move into GRC or ticketing without re-keying?
  • Can you see the full decision history for one supplier?

‍

What will TPRM software really cost to run?

The real cost of TPRM software is the licence plus everything the platform leaves your team to do: implementation, integrations, data feeds, services, supplier chasing, evidence review and alert triage. Compare three-year operating cost and time to useful supplier coverage, not the subscription price.

The cheapest subscription can be the most expensive programme. A low-cost tool that leaves your team sending questionnaires, chasing suppliers and reconciling evidence by hand moves cost from the invoice to your headcount, and headcount is what most security teams are shortest of. Pricing models also vary by type.

Governance suites tend to price by module and user, ratings platforms by the number of organisations monitored, and workflow platforms by supplier volume, with managed assessments on top. Some models also charge suppliers, which affects participation as much as budget. Each of these models is reasonable, but they scale differently.

A platform priced per monitored supplier gets more expensive exactly as your coverage improves. Ask each vendor to price your actual supplier population across three years, including services and the tier you'll need in year two. Set that price against the internal time the platform will remove and the time it won't.
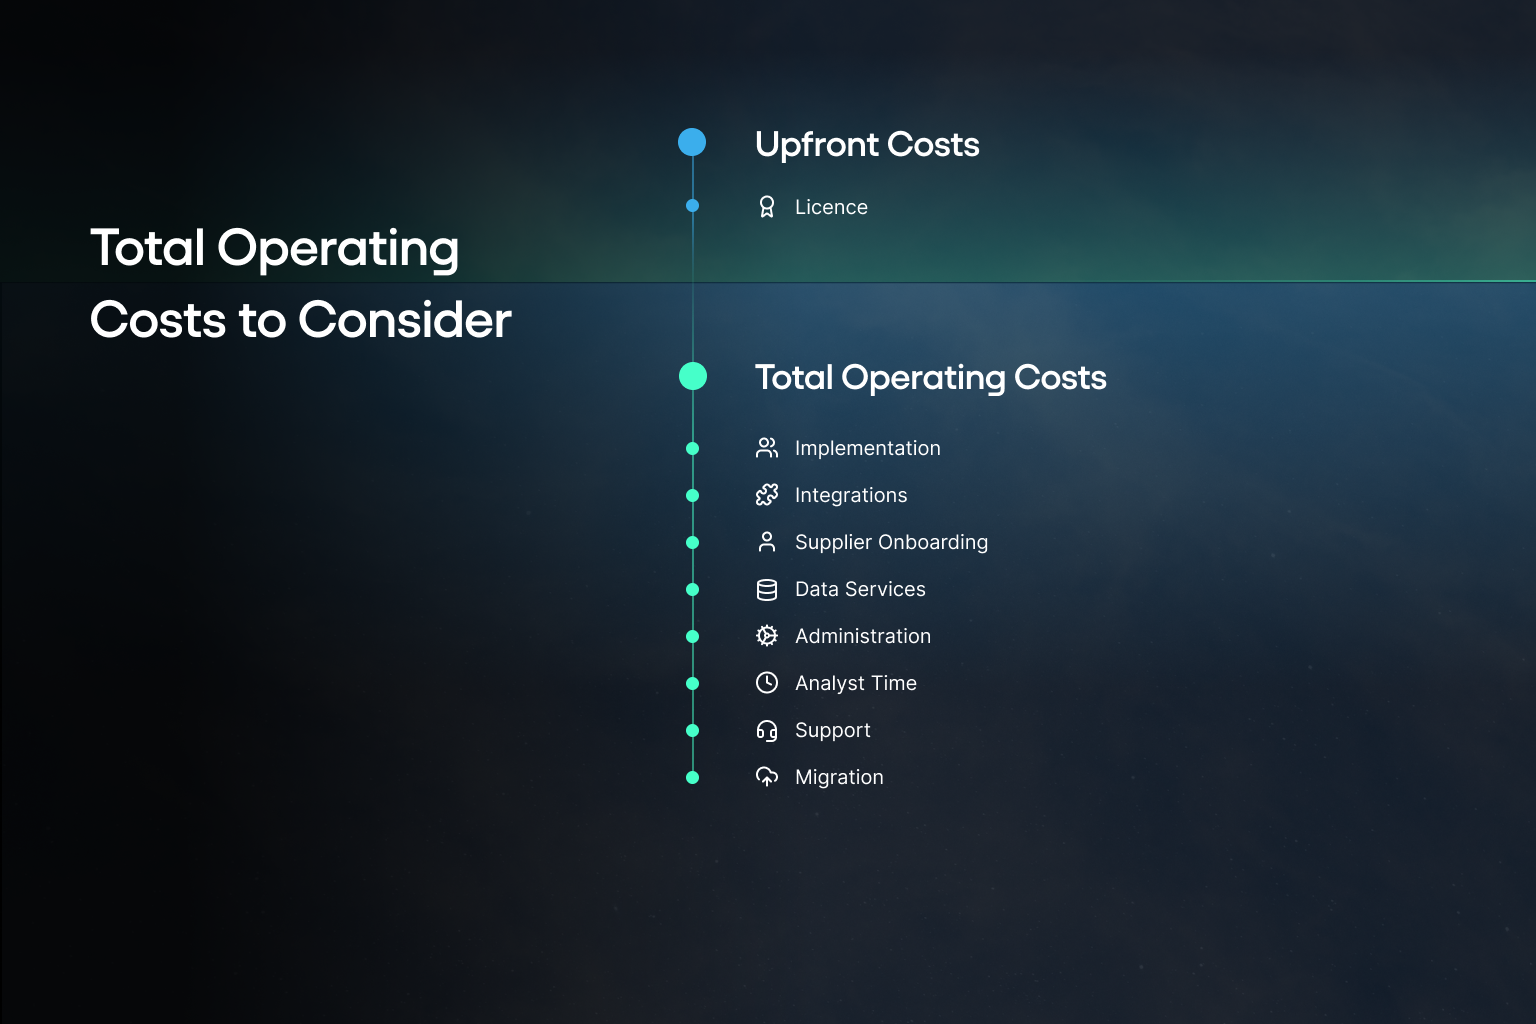
Third-party risk management software costs

Time to launch isn't time to value

Implementation plans usually measure configuration: the platform is set up, users are trained and questionnaires are loaded. Value starts later, when priority suppliers are actually covered with current evidence. How long that takes depends mostly on supplier participation and on how much usable evidence already exists, not on the platform's setup checklist.

Ask for a week-by-week plan that names the date your critical suppliers will be assessed, who does the work in each week, and what happens to suppliers who haven't responded by then. A quote that only covers configuration is half a plan.

Contract and exit checks

  • Data export: which data you can take, in which formats and at what cost, including evidence files and decision history
  • Supplier limits: what happens to the price when your supplier count grows past the quoted tier
  • Renewal terms: caps on price increases, and notice periods
  • Module boundaries: whether every capability shown in the demo is in the package you're being quoted
  • Exit support: how long you keep access after giving notice, and what help you get migrating

A higher licence fee can still be the cheaper programme if it removes enough internal work. That's why the comparison has to cover three years and include your team's time.

‍

TPRM software trade-offs to weigh before you shortlist

Every type of TPRM software trades one strength for another: configurability against upkeep, breadth against depth, scale against evidence quality. The right choice depends on which side of each trade-off your programme can live with. Naming those trade-offs early saves time later in the evaluation.

Vendor comparisons tend to present capabilities as if they add up but, in practice, they pull against each other. A platform that lets you build any questionnaire and scoring model you like also needs someone to maintain them. It also makes results harder to compare across suppliers, and harder for suppliers to reuse. And a platform that standardises everything is quicker to run and easier for suppliers, but may not satisfy a bespoke control framework.

Neither is better in general. Decide in advance which side of each trade-off you're prepared to accept, and write it into the requirements. That way the evaluation team isn't swayed by whichever demo shows the most impressive version of the side you didn't need. Trade-offs also shift as a programme matures, so revisit them at renewal rather than assuming the first answer still holds.

Trade-offs

Six trade-offs to settle before the demos

Decide which side you can live with, then write it into your requirements.

  • Configurability

    Standardisation

    Lean configurable whenYou have bespoke control weighting, a mature methodology and dedicated administrators.

    Lean standardised whenYou want comparable results, less upkeep and evidence suppliers can reuse.

    Watch for: configuration becoming permanent maintenance work.

  • Breadth

    Depth

    Lean broad whenConsolidation and one system of record across risk types matter most.

    Lean deep whenSupplier security assurance is the core problem to solve.

    Watch for: the answer is often integration, not replacement.

  • Outside-in scale

    Inside-out evidence

    Lean outside-in whenYou need to triage thousands of suppliers quickly with little supplier effort.

    Lean inside-out whenCritical suppliers need evidence about internal controls.

    Watch for: most programmes need both, so plan how they'll be combined.

  • Managed outcome

    Internal control

    Lean managed whenPeople and capacity are the binding constraint.

    Lean internal whenYou need direct access to live evidence and decisions.

    Watch for: who holds the programme's knowledge if the service changes.

  • Fast launch

    Enterprise governance

    Lean fast whenA small team needs coverage of critical suppliers now.

    Lean governance whenSeveral business units need complex approvals and audit trails.

    Watch for: buying for future maturity can stall the programme you have today.

  • Shared network

    Supplier-by-supplier collection

    Lean network whenDuplicated requests are the main burden and many suppliers are already represented.

    Lean supplier-by-supplier whenYour supplier base is niche or you need bespoke questionnaires for each supplier.

    Watch for: test coverage against your actual supplier list, not the vendor's headline figures.

‍

Questions to ask every TPRM vendor

The most useful questions for a TPRM vendor test what happens beyond the demo: where evidence comes from, how suppliers participate, what "continuous" means, what happens after a finding and what the platform will cost over three years. Weak answers tend to sound confident and general, so ask vendors to show rather than tell.

Use the same questions with every vendor, and send them in writing before the demo so the session shows the answers rather than describing them. Score each answer against your weighted criteria, not against how polished the presentation was. Where a vendor can't answer, record it as a gap rather than a "to follow", because follow-ups have a way of never arriving before the contract does.

The weak answers listed below don't prove a platform is wrong for you. They're prompts for a follow-up question, to see whether the vendor can get specific. A vendor that answers "it depends" and then explains exactly what it depends on is usually giving you a better answer than one with a confident yes to everything. Bring the people who will run the process into these sessions too, since they'll recognise a vague answer about supplier chasing or alert triage faster than the buying team will.

Vendor question bank

18 questions to ask every TPRM vendor

With the weak answers worth following up.

01Fit and centre of gravity
  1. What problem was the platform originally built to solve?

    Weak answer: "All of them." Every platform has a centre of gravity, and a vendor that can't name theirs hasn't thought about where it's weakest.

  2. Which organisations like ours chose you, and why did similar ones choose someone else?

    Weak answer: No explanation of why deals are lost.

  3. What work will still sit with our team after go-live?

    Weak answer: "The platform automates that," with no detail on who reviews, chases and decides.

02Evidence
  1. Where does each piece of evidence come from: supplied, observed, purchased or inferred?

    Weak answer: A single score with no visible sources behind it.

  2. Who validates evidence, and how does a supplier dispute a finding?

    Weak answer: Disputes handled by email or support ticket, outside the record.

  3. Is assessment at company, product or service level?

    Weak answer: Company level only, regardless of which service you actually buy.

03Supplier participation
  1. What does a supplier have to do, and does it cost them anything?

    Weak answer: A new questionnaire for every customer, with no reuse.

  2. What are your invitation acceptance and completion rates for customers like us?

    Weak answer: Anecdotes instead of figures.

  3. What happens when a supplier refuses or can't use the platform?

    Weak answer: "That rarely happens."

04Monitoring and change
  1. Which kinds of continuous monitoring do you provide, and which evidence updates without anyone acting?

    Weak answer: "Real-time" without saying what is real-time.

  2. What triggers a reassessment, and who defines the triggers?

    Weak answer: Reassessment on a fixed schedule only.

  3. How do existing suppliers come into the process, not just new ones?

    Weak answer: A migration plan that ends at importing a spreadsheet.

05Findings and workflow
  1. Can you show one finding from detection to closure or accepted risk?

    Weak answer: The demo stops at a score or dashboard.

  2. How does the outcome reach our GRC or ticketing system?

    Weak answer: "Through our API," with no working example.

  3. Do accepted risks expire and come back for review?

    Weak answer: Acceptance recorded once and never revisited.

06Commercials and exit
  1. What will our actual supplier population cost over three years, including the year-two tier?

    Weak answer: A year-one price only.

  2. What can we export if we leave, in what format and at what cost?

    Weak answer: Reports only, without evidence files or decision history.

  3. Is everything shown in the demo included in the package you're quoting?

    Weak answer: Hesitation, then a list of add-on modules.

Proofs of concept and references

A proof of concept should use your suppliers, not the vendor's sample data. Include a critical supplier, a small one and one that's slow to respond, and measure what changes: how long coverage takes, how much your team had to do, and what the suppliers thought of the experience. A short pilot with real suppliers tells you more than a longer series of polished demos.

For references, ask for a customer of similar size and sector that has been live for more than a year. Ask what they'd do differently, what still takes more time than expected, and whether supplier participation matched what they were promised.

‍

Which TPRM tools fit which team?

There is no universally best TPRM software. Governance-led organisations are usually best served by a governance suite, security teams monitoring very large portfolios by a ratings platform, and mature programmes with bespoke methodologies by a configurable workflow platform. Teams whose hardest problems are repeated supplier requests, participation and visibility beyond direct suppliers should start with a network-led platform.

If the main requirement is enterprise governance, start with a governance suite, and accept that supplier-security depth may need a specialist platform feeding into it. If it's broad outside-in monitoring, start with a ratings platform and plan how critical suppliers will get deeper evidence.

If a dedicated team runs a detailed, bespoke assessment methodology, a configurable workflow platform will fit that methodology best. If the job is mainly sharing and reusing compliance evidence, an evidence and compliance platform may be all you need for now. If there's nobody to run the programme, a managed service is often better advice than any software.

And if the central problems are repeated supplier requests, low participation, stale internal-control evidence and slow exposure analysis when an incident hits, a network-led platform belongs at the top of the shortlist. Risk Ledger builds this last model.

Verdict

Where each type of team should start

Starting points, not final answers. Most mature programmes combine two types.

  • If you areA large organisation consolidating governance across many types of risk

    Enterprise governance suite

    Often paired with: a specialist platform feeding supplier-security evidence into it

  • If you areA mature TPRM function with a bespoke assessment methodology

    TPRM workflow platform

    Often paired with: a ratings feed for monitoring between reviews

  • If you areA security team watching thousands of suppliers

    Ratings and monitoring platform

    Often paired with: deeper assessment of critical suppliers

  • If you areA compliance-led organisation with light vendor reviews

    Evidence and compliance platform

    Often paired with: little else, until supplier risk grows

  • If you areA lean security-led team facing repeated supplier requests, low participation and a need to see beyond direct suppliers

    Network-led TPRM platform

    Often paired with: an existing GRC platform as the system of record

  • If you areA team without the capacity to run a programme

    Managed service, on any type

    Often paired with: direct access to the evidence and decisions it produces

Most mature programmes end up combining two of these, usually a system of record and a specialist layer. Which pair you choose matters less than being clear which tool owns which job, so evidence, findings and decisions don't end up split across systems that nobody reconciles.

‍

How we approach TPRM at Risk Ledger

Risk Ledger is a network-led TPRM platform for security teams. Suppliers maintain one standardised security profile and share it with each customer who needs it. Every customer applies its own policies and risk appetite to that evidence, and the connections between organisations show dependencies beyond direct suppliers.

We built Risk Ledger around one observation: most of the work in a traditional TPRM programme is duplicated. The same supplier answers broadly the same questions for dozens of customers, each in a different format, and each customer chases, reviews and files the answers separately.

The evidence is out of date by the time the next cycle comes round, and none of it shows who those suppliers depend on. Better workflow software makes that process tidier but leaves the duplication in place, so we changed the evidence model instead.

A supplier completes and maintains one profile, shares it with each customer and keeps it current as things change. It's free for suppliers to take part, because charging the people you need answers from is a reliable way not to get them. Customers still make their own decisions. The profile is shared, the judgement isn't.
How it works in practice

  • Reusable supplier evidence. Suppliers complete one standardised assessment with supporting evidence, then share it with each connected customer.
  • Your policies, your decisions. You apply your own criticality, risk appetite and review requirements, and record your own decisions.
  • Direct collaboration. Questions, findings and remediation happen with the supplier, in the same place as the evidence.
  • Changes between reviews. When a supplier updates its profile or evidence expires, connected customers see it.
  • External findings in context. External observations are linked to the relevant assessment areas, so suppliers can explain or fix them. [Product to confirm exact mechanic]
  • Visibility beyond direct suppliers. Organisations connect to their own suppliers on the platform, which shows shared dependencies and concentration across your supply chain. The view covers the relationships organisations have connected, and grows as more of your supply chain joins. More than 19,000 organisations are on the network today.

We call this approach Active Supply Chain Security. The label matters less than the mechanics behind it: reusable supplier evidence, visible dependencies and a coordinated response when a shared threat appears.

How we differ from each type of tool

  • Enterprise governance suites. We're not a system of record for enterprise risk. We work alongside one, producing current supplier-security evidence and passing outcomes into it.
  • TPRM workflow platforms. These make the questionnaire process more efficient. We change who does the work, with suppliers maintaining reusable evidence instead of answering each customer separately. The trade-off is less freedom to build bespoke questionnaires.
  • Ratings and monitoring platforms. External observations are useful evidence. We combine them with supplier-provided controls and relationship context rather than relying on a score.
  • Evidence and compliance platforms. We share the reuse principle, but the profile is part of a live relationship with findings and remediation, not a published report.

When another approach may fit better

Risk Ledger is best suited to security-led teams that value supplier participation, reusable supplier evidence and visibility beyond their direct suppliers, and that want those capabilities working inside a standardised assessment process rather than a heavily configured one. Another route may fit better if:
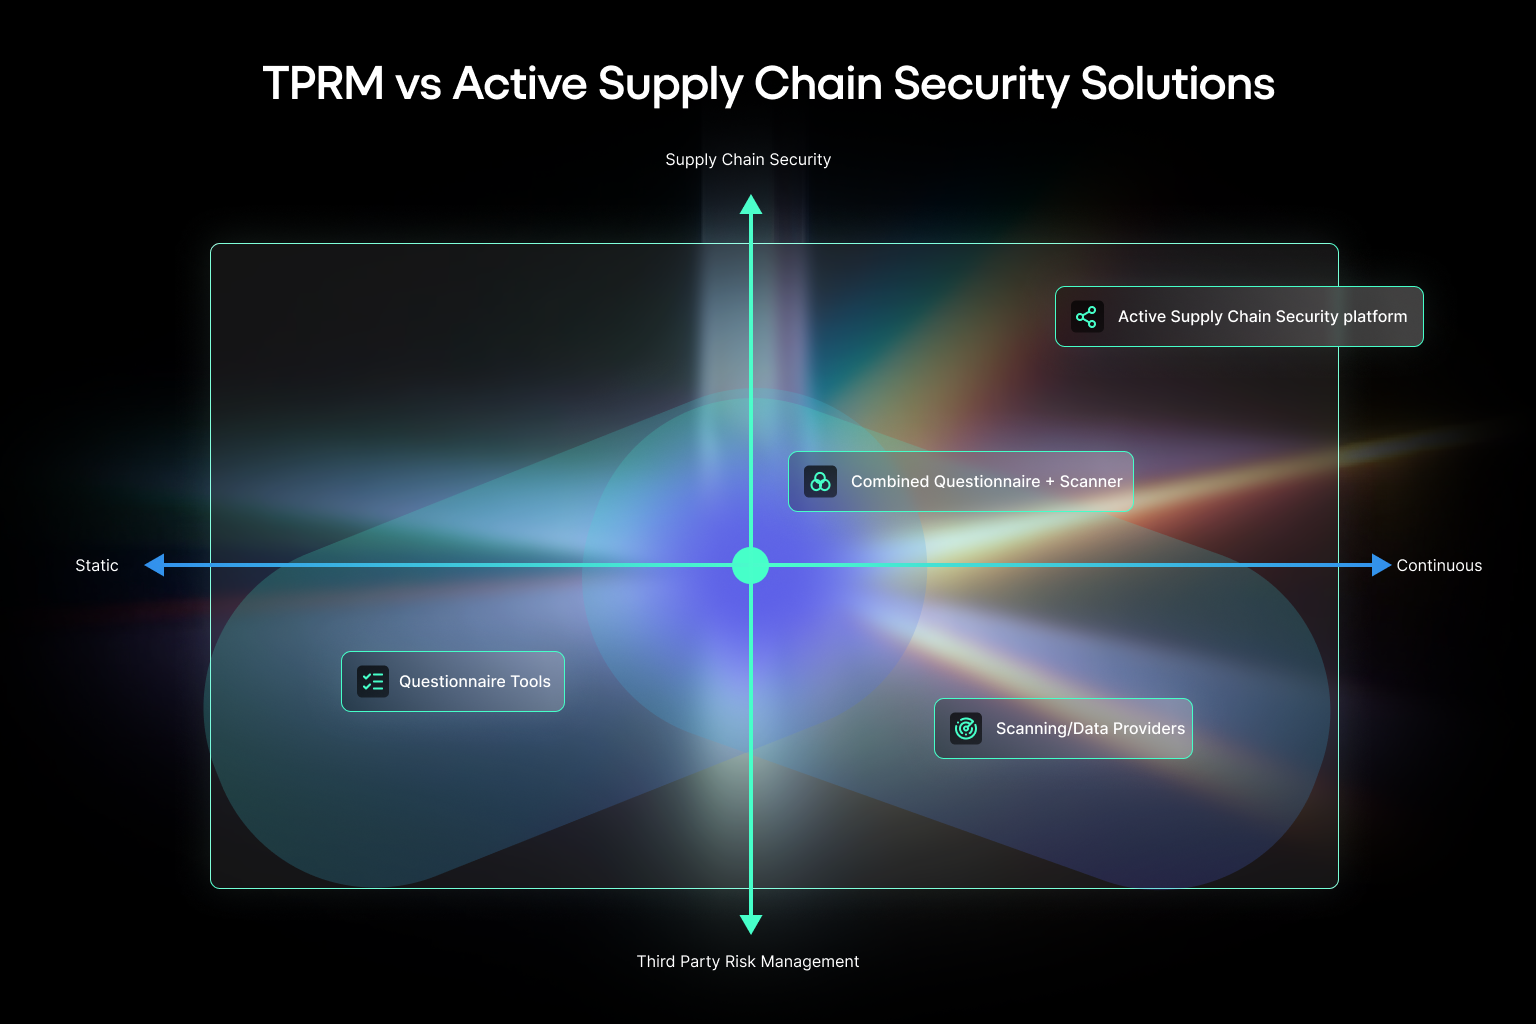
  • You want one enterprise suite covering every risk type, rather than a specialist security platform.
  • Standalone attack-surface monitoring across thousands of organisations is your main requirement.
  • You need someone to run the programme for you. We're software, not a managed service.
  • You need unrestricted bespoke questionnaires and scoring for every supplier.
  • Procurement, contracts or supplier performance are the centre of the purchase.
  • You need financial, ESG or geopolitical supplier intelligence.
  • Few of your suppliers are on the network and you can't support onboarding the rest.
TPRM Software Landscape

‍

What security teams ask next about TPRM software

‍

Third party risk management software FAQs

General

What is third-party risk management software?

Third-party risk management (TPRM) software is a category of platform that helps organisations assess, monitor and manage the risk suppliers and other third parties introduce. It brings supplier inventories, security evidence, assessments, findings and monitoring into one place, so security, procurement and risk teams can make consistent decisions from onboarding through to renewal or exit.

Is third-party risk management software the same as third-party risk assessment software?

Not quite. Third-party risk assessment software and tools handle questionnaires and evidence collection at due diligence. Third-party risk management software covers the whole supplier relationship, including monitoring, findings, remediation and reassessment after approval. G2 groups many of these platforms as third party and supplier risk management software, so check what a product does after a supplier is approved rather than relying on the label.

What is the difference between third-party risk management software and GRC software?

GRC software governs risk, controls, policy and audit across the whole organisation, and supplier risk is often one module within it. Third-party risk management software specialises in supplier assessment, evidence, findings and monitoring. Many organisations use both, with the GRC platform as the system of record and a TPRM platform producing current supplier evidence and passing outcomes into it.

Do security ratings replace supplier assessments?

No. Security ratings show what can be observed about a supplier from outside, such as exposed services or email configuration, across large portfolios with little supplier effort. They can't confirm internal controls such as access reviews or backups, or tell you why a supplier matters to you. Most programmes use ratings to monitor broadly and assessments to evidence critical suppliers in depth.

How many TPRM vendors should we shortlist?

Three is usually enough, drawn from different types of tool if you haven't yet settled on a type. More than four tends to produce shallow comparisons, because each vendor gets less time with your real suppliers. Use mandatory requirements to cut the long list, then compare the shortlist on the same weighted criteria and the same supplier scenarios.

Can third-party risk management software replace spreadsheets?

For most programmes beyond a small supplier population, yes. Spreadsheets work when a clear owner manages a handful of suppliers. They break down when supplier volume, evidence freshness, regulatory expectations or incident response outgrow what the team can maintain by hand, because there's no audit trail, no remediation tracking and no quick way to see which suppliers are exposed when something happens.

How much does third-party risk management software cost?

Pricing depends on the type of platform, the number of suppliers, the modules and services included, and any monitoring feeds. The licence is only part of the cost. Compare three-year operating cost: licence, implementation, integrations, data feeds and services, plus the internal time spent on supplier chasing, evidence review, alert triage and reporting, plus renewal increases and exit costs.

How long does it take to implement a TPRM platform?

Configuration can take anything from days to months, depending on the platform's complexity and your integrations. The more useful measure is time to useful coverage: the date your critical suppliers are assessed with current evidence. That depends mainly on supplier participation and on how much usable evidence already exists, so ask vendors for a week-by-week plan that names that date.

How should a small team choose third-party risk management software?

Start with the bottleneck that takes most of the team's time, often supplier chasing and manual questionnaires, and weight it heavily. Favour platforms with low administration, simple defaults and strong supplier participation over deep configurability you won't have time to maintain. If nobody has the capacity to run the programme at all, consider a managed service.

Do we still own the risk when we use a TPRM platform?

Yes. A TPRM platform supports evidence collection, assessment, monitoring and remediation, but your organisation stays accountable for accepting and managing supplier risk. Supplier risks you accept should still sit in your enterprise risk register with a named owner and a review date, linked back to the evidence in the platform.

Public sector

Should we require suppliers to use a specific TPRM platform?

Specify the assurance you need, not the tool suppliers must use to provide it. Requiring one platform can exclude or burden smaller bidders, which raises fairness concerns in public procurement. A better approach states the evidence required for each supplier tier, then accepts it through a preferred platform or an alternative route such as a completed questionnaire or a certification.

Can public sector bodies buy third-party risk management software through G-Cloud?

Often, yes. G-Cloud is the government framework for buying cloud hosting, software and support. G-Cloud 15, the first version let under the Procurement Act 2023, allows buyers to award contracts directly or after further competition. Check that the specific service is listed on the current framework, and confirm the right route with your procurement team.

Financial services

Can a TPRM platform help with DORA's register of information?

It can help maintain the data behind it. DORA requires financial entities to keep a register of all contractual arrangements with ICT third-party service providers. A TPRM platform can hold supplier details, the services they support, assessments and dependencies in one place and keep them current. Producing the register in the required format remains your responsibility, so check export fields against the current templates.

How do the UK's material third-party reporting rules affect TPRM?

From 18 March 2027, FCA and PRA rules (PS26/2 and PS7/26) require in-scope firms to notify regulators when they enter into or significantly change a material third-party arrangement, and to maintain and submit registers of those arrangements. A TPRM platform can keep that register current and record significant changes, but deciding which arrangements are material stays with the firm.

‍

Sources

NIST SP 800-161 Rev. 1, Cybersecurity Supply Chain Risk Management Practices for Systems and Organizations
NIST Cybersecurity Framework 2.0: Quick-Start Guide for Cybersecurity Supply Chain Risk Management

NCSC: The principles of supply chain security

NCSC: How to assess and gain confidence in your supply chain cyber security

NCSC: Supplier assurance questions

UK Government: Cyber Security Breaches Survey 2025/2026

CISA: Supply Chain Risk Management Essentials

ENISA: Good Practices for Supply Chain Cybersecurity

Gartner: Third-party risks are driving growth and maturity in TPRM technology

EY: Global Third-Party Risk Management Survey

Federal Reserve: Interagency Guidance on Third-Party Relationships

Bank of England and PRA: Outsourcing and third-party risk management

Blog

Download for free

Pattern Trapezoid Mesh

Get the security manager's briefing

Monthly research, case studies and practical guides you won't find anywhere else.

Join thousands of security managers turning their TPRM programmes into success stories.